ACH and wire fraud controls must operate in the short interval between payment initiation and release. Static limits and after-the-fact reports are not enough when criminals exploit compromised credentials, changed contact information, new payees, social engineering, and weak callback procedures. The control design must connect data, decision, operations, and customer contact in real time.
Build the decision from payment context
Customer and account
Consider tenure, normal payment behavior, balance movement, recent profile changes, authentication events, entitlements, and prior fraud history.
Payment and payee
Evaluate amount, timing, channel, destination, payee age, beneficiary changes, velocity, return history, geography, and relationship context.
Device and session
Use device familiarity, network reputation, session integrity, location, concurrent access, navigation, and proximity to recovery events.
Operational context
Include approval authority, dual control, call-back status, business purpose, supporting evidence, queue capacity, cutoffs, and recovery windows.
Separate detection from the permitted action
The same risk signal may justify different actions by payment type, amount, customer, and time to release. Define when to allow, step up, hold, route for review, require dual approval, complete a trusted-channel callback, reject, or escalate. Preserve the rule, facts, owner, decision, and timestamps.
Make callbacks resistant to social engineering
Do not rely on contact information changed in the same session or supplied with the payment request. Define trusted contact sources, separation of duties, authentication questions that do not expose sensitive data, unavailable-customer procedures, and evidence of the completed verification.
Design the queue around time at risk
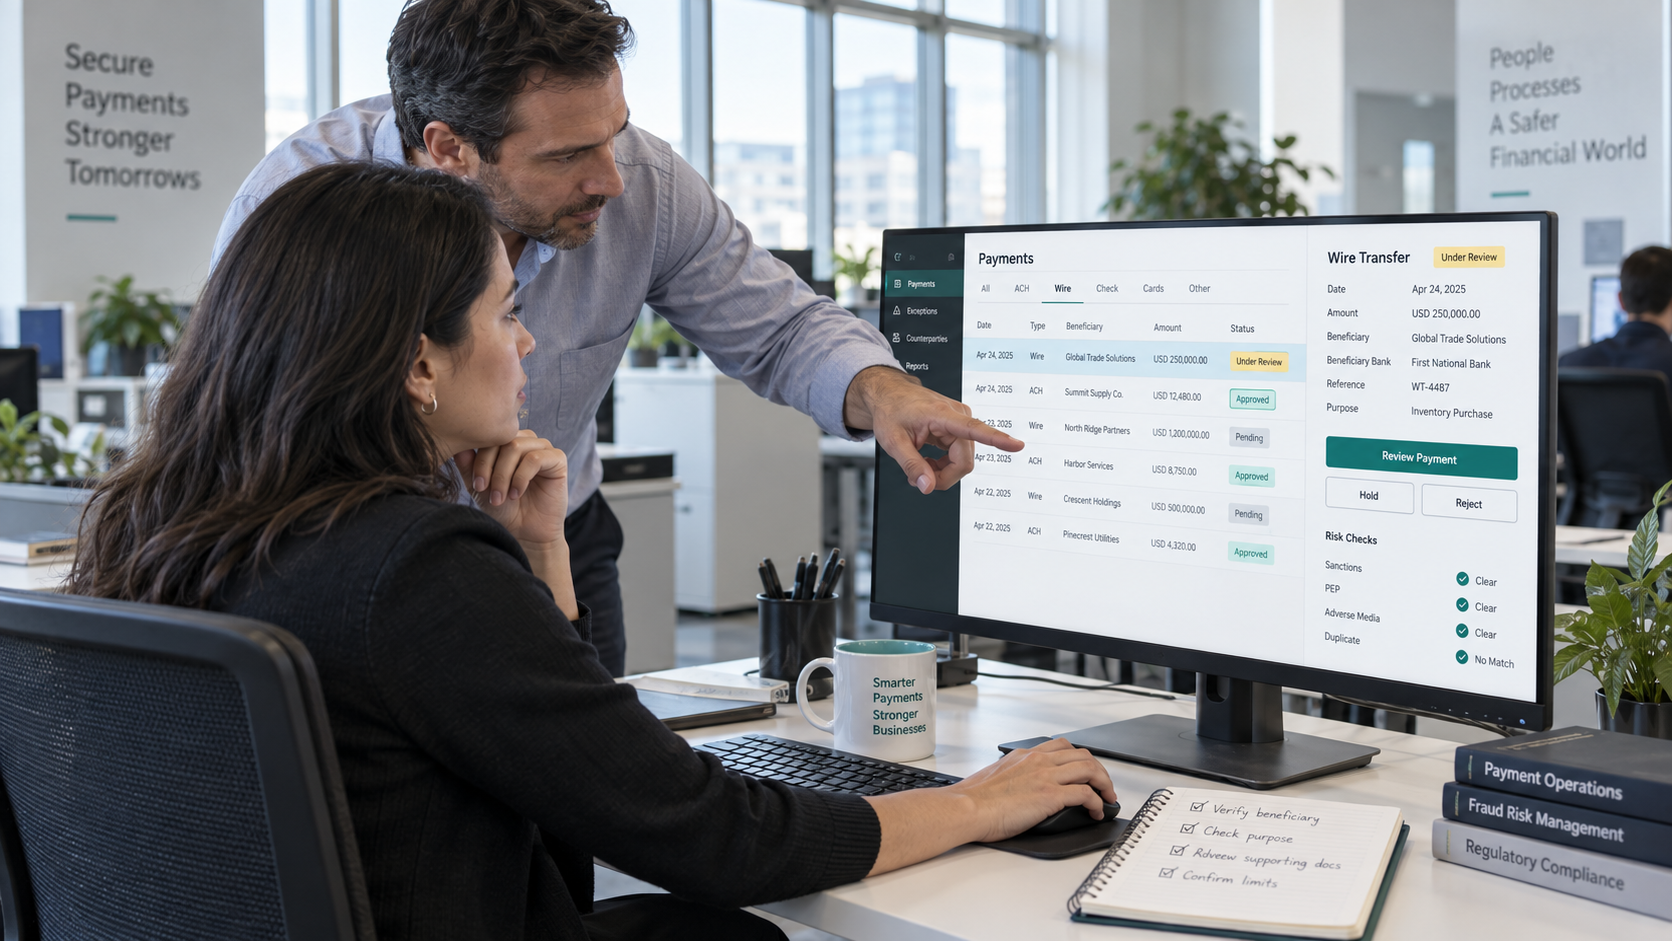
Prioritize cases using severity and time remaining before release, not arrival order alone. Show the investigator the signal timeline, payment details, relationship history, supporting documents, linked accounts or devices, and the next authorized actions. Escalate automatically as cutoffs approach.
Measure the end-to-end control
Track prevented loss, unauthorized-payment loss, holds, confirmation rates, false positives, review time, callback completion, missed cutoff, customer impact, recovery, rule changes, and repeated scenarios. Reconcile decisions with payment release and settlement so control reports reflect what actually happened.
A practical implementation sequence
- Map payment journeys, release points, cutoffs, authorities, existing controls, and confirmed fraud scenarios.
- Connect identity, device, account, payee, transaction, and customer-contact data with explicit latency and quality expectations.
- Define risk-tiered actions, trusted callback procedures, queue ownership, and escalation.
- Run observation and parallel-review pilots before introducing automated holds or declines.
- Validate outcomes continuously and govern rule, model, threshold, and workflow changes.