Cybersecurity
Cicrim helps regional and community banks reduce cyber risk with pragmatic, regulator-aware security programs. We assess, harden, monitor, and validate controls so your institution can defend against real threats and prove it to examiners and auditors.
Banks don’t need more cybersecurity. They need prioritized, provable controls that reduce real-world risk and withstand examiner scrutiny, aligned to FFIEC expectations and mapped to NIST CSF / CIS Controls for clarity and governance.
Proactively protect the confidentiality, integrity, and availability of banking systems.
Modern attacks exploit gaps in identity, vendor access, configuration drift, and inconsistent control ownership, not just elite hacking. For regulated institutions, the impact is amplified: Operational disruption, reputational harm, customer risk, and heightened regulatory attention.
Cicrim supports security leaders with clear roadmaps and hands-on execution, from risk assessments and control design to validation, monitoring, and board-ready reporting. We focus on measurable outcomes: Reduced exposure, faster detection and response, and clean audit trails.
If your goal is to pass exams with confidence and materially reduce cyber risk, without creating paper security. Cicrim is built for that.
Our solutions
Practical, bank-ready cybersecurity services designed to reduce risk, strengthen controls, and satisfy examiners.

Risk, program & technical assessments
- FFIEC-aligned bank cybersecurity maturity assessment mapped to NIST CSF and CIS
- Risk assessment refresh with control ownership, evidence expectations, and remediation plan
- Vulnerability assessment and prioritization focused on attack paths & critical assets
- External, internal and web application penetration testing with actionable remediation guidance
- Cloud & identity security posture reviews across MFA, conditional access, privileged access and logging
- Incident response readiness review across runbooks, detection coverage, escalation and vendor coordination
Governance, compliance & assurance
Banking regulatory alignment
- FFIEC CAT modernization mapping to NIST CSF 2.0-style program structure
- GLBA Safeguards support: Control mapping, evidence, and examiner-ready narratives
- Board/committee reporting: KRIs, posture trending, and risk acceptance documentation
Assurance & validation
- SOC 1 and SOC 2 readiness support across control design, evidence routines and gap closure
- PCI DSS support for card environments across scope clarity, compensating controls and validation
- Policy and standard rationalization for shorter, clearer, enforceable and measurable requirements
Secure AI enablement
- AI usage policy & guardrails for regulated environments
- Model risk coordination with security controls for logging, access and change management
- Foundational monitoring for AI services across security signals & auditability
Featured resources
Quick, high-value guidance designed for bank CISOs, CIOs, risk leaders, and compliance teams, focused on defensible controls, clear evidence, and exam-ready outcomes.
90-day cyber readiness sprint
A structured, bank-ready plan to stabilize your security posture fast. We focus on the highest-impact controls first: Identity, logging, vulnerability remediation, incident readiness, and evidence routines that map to FFIEC expectations.
Ideal for institutions preparing for an exam, recovering from findings, or rebuilding control ownership.
Days 1–30: Assess and prioritize
Confirm critical services, control owners and the highest-priority gaps. Baseline identity, logging, vulnerabilities and incident readiness.
Output: Agreed scope, prioritized risks and accountable owners.
Days 31–60: Implement and exercise
Address agreed control gaps, establish monitoring routines and exercise incident escalation with the responsible teams.
Output: Implemented changes, exercise findings and an evidence register.
Days 61–90: Verify and sustain
Validate completed work, document remaining risks and transfer recurring review and response routines to named owners.
Output: Verification records, an open-issue plan and a sustainable operating cadence.
Incident response tabletop kit
Run an examiner-friendly tabletop exercise with realistic banking scenarios covering credential compromise, wire fraud enablement, ransomware, vendor breaches and cloud misconfiguration. Includes objectives, roles, timelines, decision points, and after-action templates.
Identity hardening checklist
A practical checklist for bank identity and privileged access controls, MFA coverage, conditional access, admin role hygiene, service accounts, logging, and break-glass practices.
Secure AI: Controls & monitoring
An overview of security controls and monitoring expectations when deploying AI capabilities in a regulated bank environment, including access, logging, change control, data handling, and basic observability signals.
Who we serve
Cicrim is purpose-built for financial services, where cyber risk is business risk and evidence matters.
Community Banks
Exam-ready controls, practical remediation, and board-level reporting with clear KRIs.
Credit Unions
Security maturity, identity hardening, and incident readiness without unnecessary overhead.
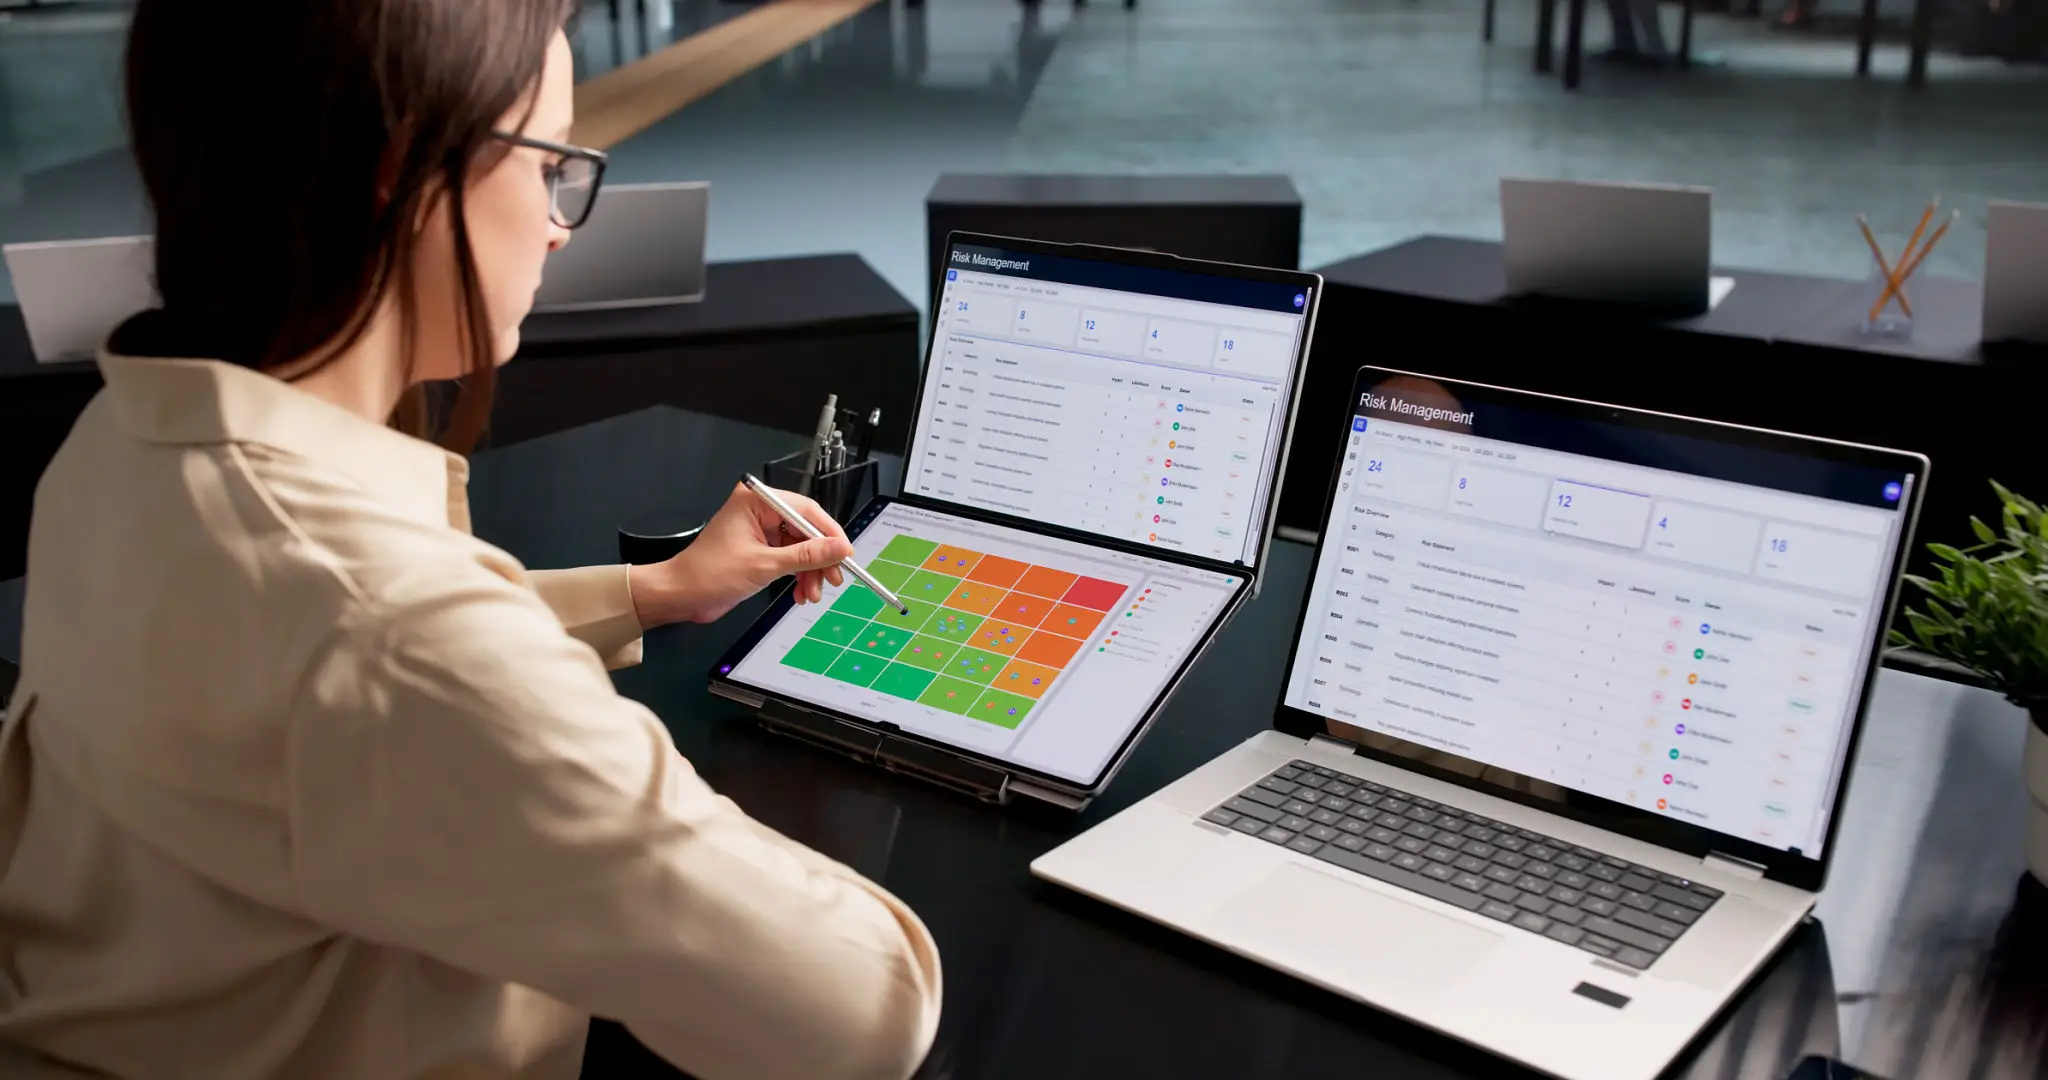
Third-Party Risk Management
Connect vendor due diligence, continuous monitoring, accountable exceptions, and examiner-ready evidence.
Zscaler
Connect zero-trust security to cloud, AI, data, third-party access, and accountable banking operations.
Cloud Services for Regulated Banking
Align cloud architecture, security, resilience, data controls, and operating ownership for regulated workloads.
Bank Compliance & Risk Readiness
Connect regulatory expectations to operating controls, evidence, accountable owners, and sustainable routines.
Cicrim helped us turn examiner feedback into a prioritized plan we could execute. Within one quarter, our identity controls and evidence routines improved materially, and our leadership team finally had clear, credible security reporting.CISO, U.S. community bank