AI Compliance Solutions
Automate and enhance regulatory monitoring, controls testing, and examiner-ready reporting, without adding headcount.
AI Compliance Solutions

Bank Compliance & Risk Readiness
Connect regulatory expectations to operating controls, evidence, accountable owners, and sustainable routines.
Regulatory Compliance
Move from periodic exam preparation to continuous, evidence-centered compliance operations.


Automate and strengthen regulatory oversight
Cicrim’s AI Compliance Solutions help community and regional banks reduce manual effort, improve traceability, and confidently demonstrate control effectiveness. We combine compliance domain expertise with practical automation to turn regulatory expectations into repeatable workflows: Monitoring, testing, remediation tracking, and documentation, all built to be audit-ready.
Our approach is designed for real bank constraints: Limited bandwidth, multiple systems of record, and increasing expectations around vendor risk, model risk, cybersecurity, and consumer compliance. We help you implement controls and evidence practices that scale with growth while maintaining a strong relationship with examiners.
Whether you’re modernizing your governance program, deploying responsible AI, or simply trying to reduce the scramble before exams, Cicrim provides a clear path to continuous compliance, with measurable improvements in cycle time, coverage, and transparency.
What Cicrim delivers
A practical, examiner-aware compliance automation program, designed around your bank’s policies, risk appetite, and technology stack.
Continuous monitoring & alerts
Detect exceptions, drift, and policy violations across key processes with configurable thresholds, owner routing, and clear audit trails.
Controls testing automation
Automate sampling, evidence requests, and documentation for recurring controls, reducing cycle time while improving consistency.
Evidence management
Centralize artifacts, map evidence to controls, and maintain exam folders by regulation, domain, or exam scope.
Policy & procedure intelligence
Keep policies current with structured reviews, change logs, and AI-assisted comparisons that highlight what changed and why it matters.
Vendor & third-party oversight
Automate questionnaires, evidence validation, risk scoring, and renewal triggers, aligned to your TPRM standards and examiner expectations.
Examiner-ready reporting
Generate consistent narratives, findings summaries, and status dashboards that tie directly to controls, evidence, and remediation actions.
AI compliance hot topics
Compliance leaders are navigating a changing landscape: AI governance, cyber and third-party risk, faster regulatory change, and increasing expectations for documented control effectiveness. These are the themes banks are prioritizing right now.
Responsible AI governance
Establish clear ownership, policies, and controls for AI use cases, including approval workflows, data lineage, human-in-the-loop review, and ongoing monitoring for drift and bias.
Explore governance approach
Model risk management
Build inventories, tiering, validation schedules, and documentation packages that align to bank governance requirements and examiner expectations, including AI/ML-specific controls.
Learn about MRM support
Cyber & access controls
Map access, logging, and configuration controls to evidence sources so audits and exams don’t turn into email hunts. Build repeatable testing and attestation workflows.
Review cyber control guidance
Change management
Translate policy updates into actionable control changes. Track who approved what, when it changed, and where evidence lives, preserving a clean audit trail over time.
See policy change controls in practice
Evidence automation
Automate evidence requests, classify artifacts, and link them to controls and findings. Maintain consistent naming, retention, and versioning so you can answer examiner questions quickly.
See evidence automation in practice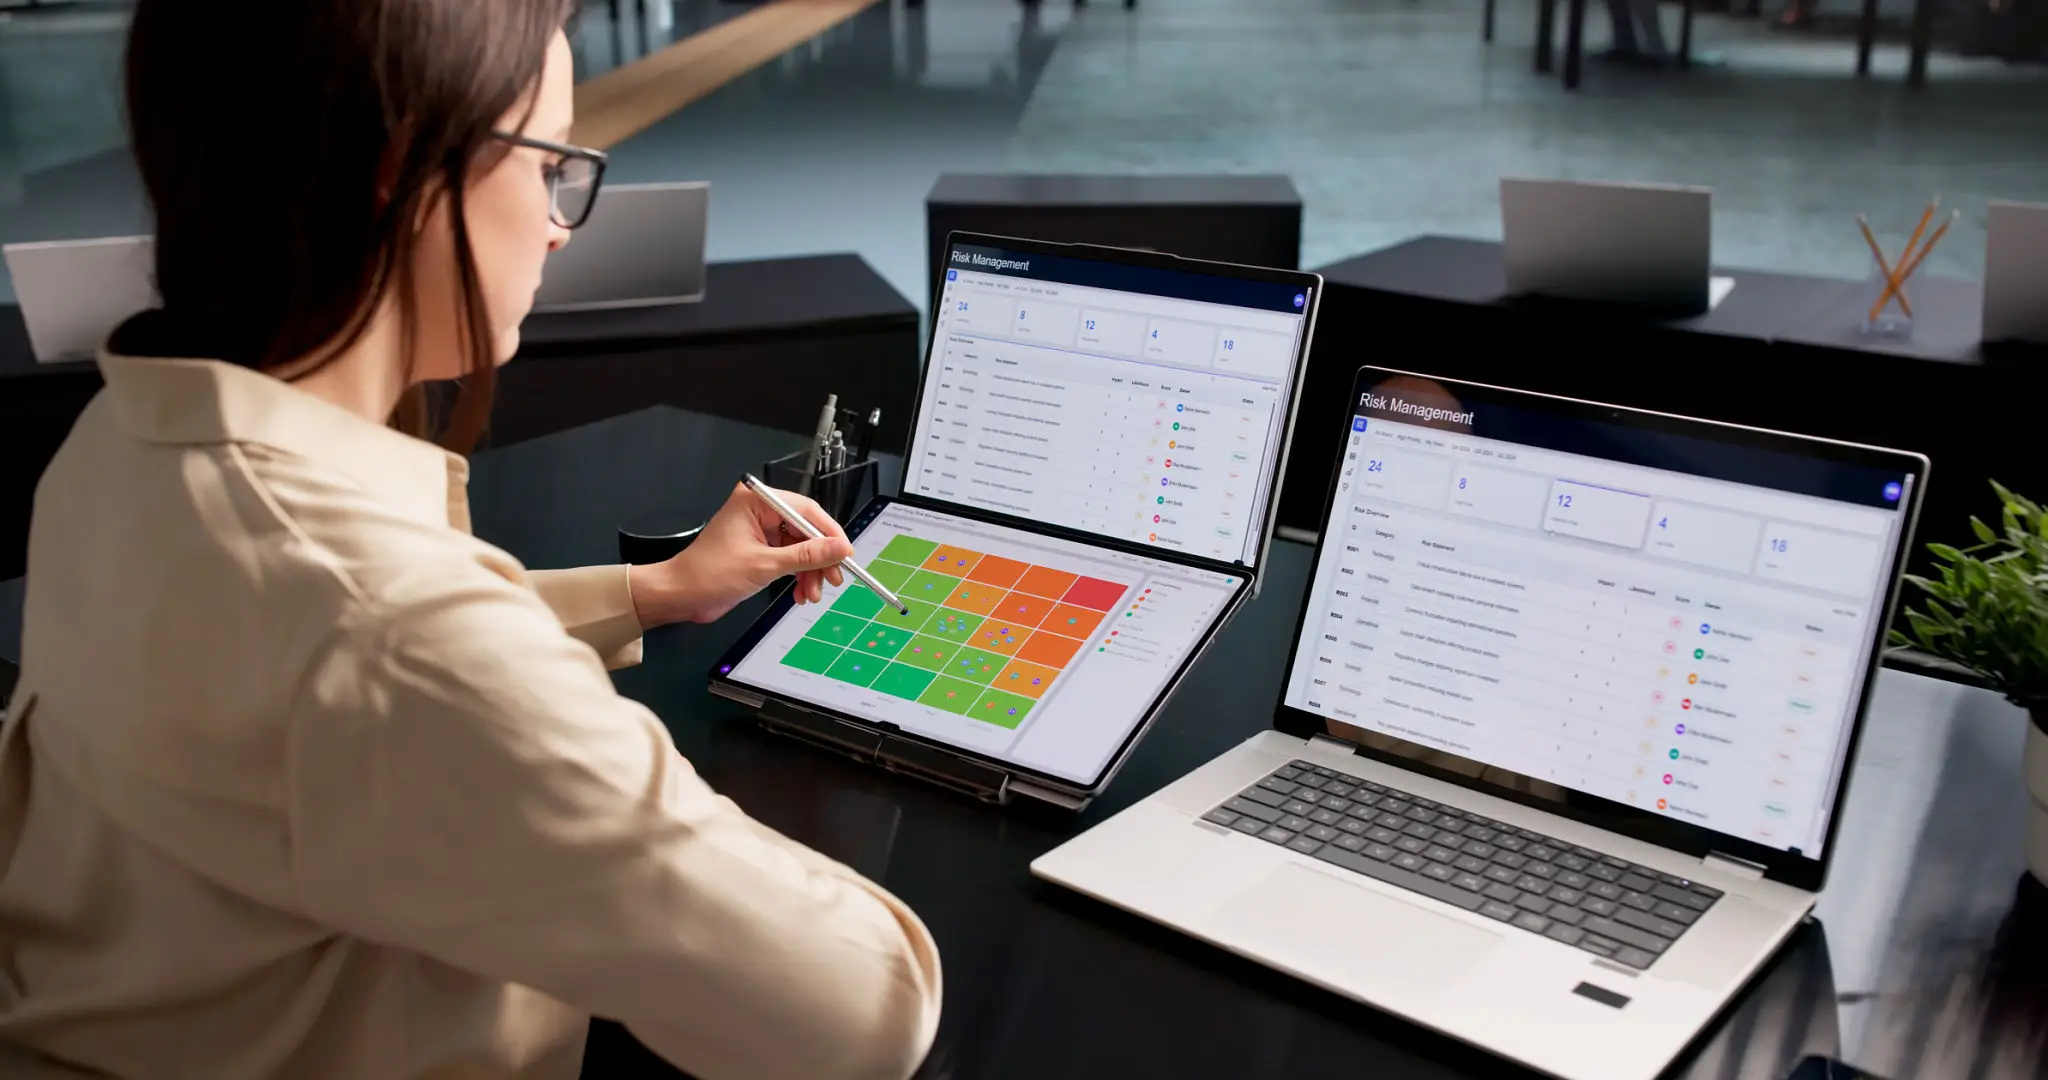
Third-party risk
Standardize due diligence and ongoing monitoring. Improve response quality and reduce turnaround time with structured questionnaires and evidence validation workflows.
See TPRM workflow options
Consumer compliance
Automate documentation and testing around disclosures, servicing, complaint management, and marketing review workflows, improving consistency and reducing rework.
Explore regulatory compliance
Audit & exam readiness
Build repeatable packages for governance, controls, evidence, and remediation tracking, and keep them current so you’re always ready for questions, not just during exam season.
Use the exam readiness guideGuiding insights


Industry spotlight
Cicrim specializes in financial services, with deep experience in bank governance, compliance, and technology modernization. We also support bank-adjacent organizations where regulated controls and evidence standards are essential.
Banking
Modern banking compliance requires strong governance, traceable controls, and rapid response to changing regulatory guidance. Cicrim helps banks establish an AI-enabled compliance operating model that improves control effectiveness and reduces manual workload.
Explore Cicrim services
Credit unions
Credit unions balance growth with tight operating budgets. We implement compliance automation that improves coverage and documentation quality while keeping processes simple for lean teams.
Talk to Cicrim
Fintech partners
Fintechs integrating with banks need strong control environments, data governance, and vendor oversight. Cicrim helps teams build compliance-by-design processes that reduce integration friction and improve trust.
Explore partnerships
BaaS programs
BaaS expands product reach, and compliance complexity. Cicrim helps banks structure partner controls, monitoring, and reporting with clear responsibilities and fast evidence production.
Discuss BaaS oversightOur strategic alliances
Compliance platforms & workflow tooling
Cicrim works alongside your existing GRC, ticketing, document management, and data platforms. We design integrations and workflows that improve evidence collection and reporting, while keeping governance and ownership clear.
If you’re selecting a new platform or modernizing your stack, we help you define requirements, evaluate fit, and implement the operating model so the tooling actually delivers measurable outcomes.
Cloud & security foundations
AI compliance depends on strong security and data governance. Cicrim helps banks implement encryption, logging, least-privilege access, retention, and monitoring patterns that support both compliance and engineering velocity.
Build a regulator-ready evidence pack: Structure, ownership, and proof
Build consistent evidence packs, control narratives, and remediation status dashboards that tie directly to your policies and testing results.
Third-party risk oversight: A practical operating model
Standardize due diligence and ongoing monitoring with workflows that reduce back-and-forth and improve evidence quality.
Regional bank automates regulatory evidence and examiner reporting
A structured roadmap to move from manual compliance to continuous oversight, covering governance, workflows, data, and reporting.
What bank leaders want
“We need compliance to be continuous, not a periodic scramble. The right automation makes our team faster, improves documentation quality, and gives examiners confidence in our controls.”
Faster evidence collection
Reduce evidence cycle time by standardizing requests, automating routing, and linking artifacts to controls.
Clear audit trails
Keep changes, approvals, and test results traceable across teams and time, improving defensibility.
Less rework
Eliminate duplicate effort with reusable exam folders and standardized narratives tied to evidence.
Higher confidence
Improve control coverage and issue detection so management and boards see risk sooner, and act faster.
Continuous compliance monitoring
What does continuous mean in compliance?
It means defining measurable control signals, monitoring them continuously, and routing exceptions to owners with clear remediation workflows. Instead of relying on periodic sampling alone, you gain earlier detection, better documentation, and a stronger narrative for boards and examiners.